Introduction to Hack A Binary Without Source Code Objdump Ghidra Reverse Engineering %e2%80%94 Lab 3
Looking for the latest information on Hack A Binary Without Source Code Objdump Ghidra Reverse Engineering %e2%80%94 Lab 3? We've gathered comprehensive data, records, and insights about Hack A Binary Without Source Code Objdump Ghidra Reverse Engineering %e2%80%94 Lab 3.
Important Facts
Explore the key sources for Hack A Binary Without Source Code Objdump Ghidra Reverse Engineering %e2%80%94 Lab 3.
Recent Updates
Stay updated on Hack A Binary Without Source Code Objdump Ghidra Reverse Engineering %e2%80%94 Lab 3's latest milestones.
Ghidra Automotive ECU hacking class (Bosch MED17, Infineon Tricore)
Reverse Engineering an Encryption Algorithm | Ghidra Binary Patching Lab
Reverse Engineering a C Program in Ghidra | Step-by-Step Binary Analysis for Beginners
HackadayU: Reverse Engineering with Ghidra Class 3
Cracking a binary with Ghidra! - Reverse Engineering 0x1
Reverse engineering with Ghidra - Reverse engineering #2
Reverse Engineering (Objection, Ghidra) Finding Parameter Flow (Hexadecimal) Communication #0x01
How Hackers Crack Any Software With Reverse Engineering
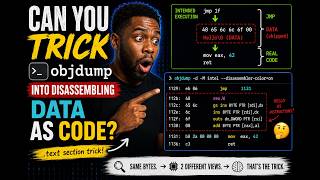
Can You Trick objdump Into Disassembling Data as Code | Binary Analysis
Reversing with Ghidra | Android UnCrackable Level 2
How Hackers Crack ANY Software With Ghidra...(Reverse Engineering)
Detailed Analysis
Data is compiled from public records and verified media reports.
Last Updated: September 14, 2026
Summary
For 2026, Hack A Binary Without Source Code Objdump Ghidra Reverse Engineering %e2%80%94 Lab 3 remains one of the most talked-about information profiles. Check back for the latest updates.
Disclaimer: Disclaimer: All information is compiled from publicly available data, media reports, and analysis. Actual details may vary.